
Introduction
In the contemporary digital landscape, the phrase “too small to be a target” has become a dangerous fallacy for entrepreneurs. Cybersecurity for Small Businesses: Essential Tips is no longer just a technical checklist; it is a fundamental pillar of business continuity and brand reputation. According to recent industry reports, approximately 43% of all cyberattacks specifically target small businesses, yet only a fraction of these enterprises feel prepared to defend against sophisticated threats. The rise of remote work, the proliferation of Internet of Things (IoT) devices, and the increasing complexity of supply chain interdependencies have expanded the attack surface for small and medium-sized businesses (SMBs) to unprecedented levels. Cybercriminals often view SMBs as the “low-hanging fruit” of the digital economy—possessing valuable data like intellectual property, customer financial records, and employee PII (Personally Identifiable Information), but often lacking the robust security infrastructure of Fortune 500 companies. This comprehensive guide provides a deep-dive analysis into the essential strategies every small business must implement to fortify its digital perimeter and foster a culture of security.
The Evolving Threat Landscape for Small Businesses
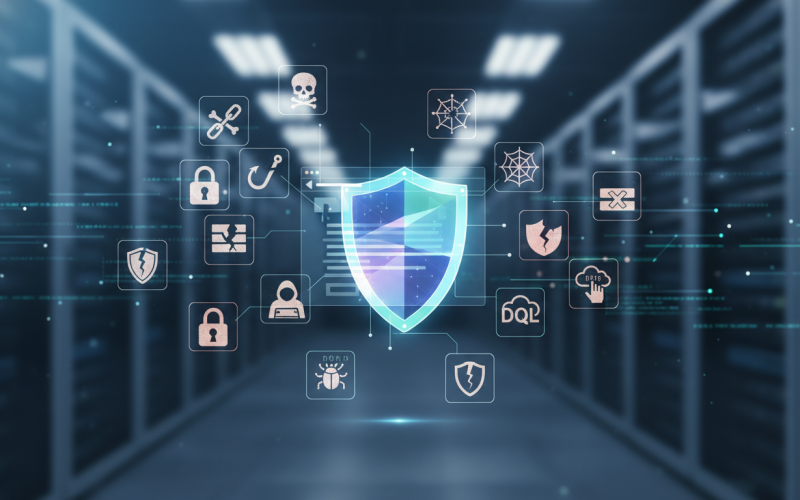
Understanding the enemy is the first step in any defensive strategy. For SMBs, the threat landscape is diverse and constantly shifting. Phishing remains the primary vector for initial access, with attackers using highly personalized social engineering tactics to deceive employees into revealing credentials or installing malware. Beyond simple phishing, we are seeing a rise in Business Email Compromise (BEC), where attackers impersonate executives to authorize fraudulent wire transfers. Ransomware has also evolved from simple data locking to “double extortion” schemes, where hackers not only encrypt files but also threaten to leak sensitive data publicly unless a ransom is paid. Furthermore, the Supply Chain Attack has emerged as a significant risk; attackers compromise a smaller, less-secure vendor to gain a foothold in the networks of larger partners. For a small business, a single breach can result in average costs exceeding $200,000, a figure that forces many out of business within six months of an incident. Therefore, implementing proactive cybersecurity measures is an investment in the company’s long-term survival.
Establishing a Human Firewall: Employee Education
Technology alone cannot secure a business if the human element is ignored. Employees are often described as the weakest link in the security chain, but with proper training, they can become your strongest line of defense. A robust cybersecurity awareness program should be mandatory and recurring. Security Awareness Training (SAT) should cover how to identify suspicious emails, the dangers of clicking on unsolicited links, and the importance of verifying unusual requests through secondary communication channels. Small businesses should conduct regular phishing simulations to test employee vigilance in a controlled environment. Education must also extend to safe browsing habits and the risks associated with using public Wi-Fi without a Virtual Private Network (VPN). By fostering a culture where security is everyone’s responsibility, businesses can significantly reduce the likelihood of a successful social engineering attack. Empowered employees are the foundation of a resilient enterprise.
Implementing Multi-Factor Authentication (MFA)
If there is one single technical control that offers the highest return on investment, it is Multi-Factor Authentication (MFA). MFA requires users to provide two or more verification factors to gain access to a resource, such as a password plus a code sent to a mobile device or a biometric scan. According to Microsoft, MFA can block over 99.9% of account compromise attacks. Small businesses should enforce MFA across all critical systems, including email accounts, cloud storage, financial software, and remote access gateways. While SMS-based codes are better than nothing, they are susceptible to “SIM swapping” attacks. For higher security, businesses should utilize Time-based One-Time Passwords (TOTP) via apps like Google Authenticator or hardware tokens like YubiKeys. Implementing MFA effectively neutralizes the threat of stolen passwords, which remain one of the most common ways hackers gain entry into corporate networks.
Securing the Network Infrastructure
A small business’s network is the nervous system of its operations, and securing it requires a multi-layered approach. The first line of defense is a Next-Generation Firewall (NGFW), which goes beyond traditional packet filtering to include deep packet inspection, intrusion prevention systems (IPS), and application-level control. For businesses with remote or hybrid workforces, a Virtual Private Network (VPN) is essential for creating an encrypted tunnel between the employee’s device and the office network. Furthermore, network segmentation—dividing the network into smaller sub-networks—can prevent an attacker from moving laterally through the system if one segment is compromised. For instance, guest Wi-Fi should always be physically or logically separated from the internal business network. Small businesses should also adopt a Zero Trust architecture, which operates on the principle of “never trust, always verify,” ensuring that every access request is authenticated and authorized regardless of its origin.
Data Encryption and Backup Strategies
Data is the lifeblood of the modern economy, and its protection is paramount. Encryption should be applied to data both at rest (stored on hard drives or in the cloud) and in transit (moving across the internet). Utilizing Advanced Encryption Standard (AES) 256-bit encryption ensures that even if data is stolen, it remains unreadable without the proper keys. Equally important is a rigorous backup strategy. Small businesses should follow the 3-2-1 rule: maintain at least three copies of your data, store them on two different media types, and keep at least one copy off-site or in a disconnected (air-gapped) environment. This is the most effective defense against ransomware; if your primary data is encrypted by hackers, you can simply restore from a clean, recent backup. Regularly testing these backups is crucial to ensure that the recovery process works as expected during a real emergency.
Cloud Security and Managed Services
Many small businesses are migrating their operations to the cloud to gain scalability and flexibility. However, the Shared Responsibility Model of cloud computing means that while the provider secures the underlying infrastructure, the business is responsible for securing the data and access within that environment. Choosing a reputable provider is vital. When migrating to the cloud, partnering with a secure provider like Sky Hostic ensures that your infrastructure is built on a foundation of security-first principles, providing peace of mind for growing enterprises. Secure cloud configurations include disabling public access to storage buckets, monitoring for unauthorized API calls, and ensuring that all cloud-based applications are updated with the latest security patches. Managed Service Providers (MSPs) can also offer specialized expertise that small businesses may lack internally, providing 24/7 monitoring and threat detection.
Endpoint Protection and Patch Management
Every device connected to your network—laptops, smartphones, tablets, and printers—is an endpoint that represents a potential entry point for attackers. Traditional antivirus software is often insufficient against modern “fileless” malware and zero-day exploits. Instead, SMBs should invest in Endpoint Detection and Response (EDR) solutions, which use behavioral analysis to identify and stop suspicious activity in real-time. Alongside endpoint protection, a strict patch management policy is essential. Software vulnerabilities are discovered daily, and developers release patches to fix them. Hackers actively scan for unpatched systems. Small businesses must ensure that operating systems, browsers, and all third-party applications are set to update automatically. Neglecting to patch a known vulnerability is like leaving the front door of your business unlocked in a high-crime neighborhood.
Incident Response Planning
Cybersecurity is about risk management, not risk elimination. Despite the best defenses, a breach can still occur. What defines a business’s resilience is its ability to respond and recover. An Incident Response Plan (IRP) is a documented set of procedures to be followed in the event of a security incident. The plan should identify the response team, define the steps for containment (stopping the spread), eradication (removing the threat), and recovery (restoring systems). It should also include a communication strategy for notifying customers, regulators, and law enforcement if necessary. Regularly “tabletop testing” the IRP allows the team to practice their roles and identify gaps in the plan. Being prepared reduces panic, minimizes downtime, and can significantly lower the total cost of a breach.
Regulatory Compliance and Legal Obligations
Small businesses must also navigate a complex web of legal and regulatory requirements. Depending on the industry and location, businesses may be subject to the General Data Protection Regulation (GDPR), the California Consumer Privacy Act (CCPA), or the Health Insurance Portability and Accountability Act (HIPAA). These regulations mandate specific data protection measures and require timely notification of data breaches. Non-compliance can result in massive fines and legal action. Implementing a robust cybersecurity framework not only protects the business from hackers but also ensures that it meets its legal obligations to protect consumer privacy. Cyber Insurance is another critical consideration, providing financial protection to cover the costs of forensic investigations, legal fees, and recovery efforts following a cyber incident.
Frequently Asked Questions
Why are small businesses targeted by cybercriminals?
Small businesses are often targeted because they typically have weaker security defenses than larger corporations, making them easier targets. They also serve as entry points into the supply chains of larger organizations and hold valuable data like customer credit card information and employee identities.
Is a simple antivirus program enough for my business?
No. Modern cyber threats are too sophisticated for traditional signature-based antivirus software. Businesses need a multi-layered approach that includes Endpoint Detection and Response (EDR), firewalls, MFA, and employee training to effectively mitigate risks.
What is the most common way hackers get into small business networks?
Phishing and stolen credentials are the most common entry points. Attackers use deceptive emails to trick employees into providing their login information or clicking on malicious links that install malware on the company network.
How often should we back up our data?
Data should be backed up at least daily, though businesses with high transaction volumes should consider real-time or hourly backups. The frequency depends on your “Recovery Point Objective” (RPO)—how much data your business can afford to lose in a disaster.
What should I do immediately if I suspect a cyberattack?
First, isolate the affected systems by disconnecting them from the network to prevent the threat from spreading. Then, follow your Incident Response Plan, notify your IT security team or provider, and document everything. Do not delete evidence, as it may be needed for forensic analysis.
Conclusion
Cybersecurity for Small Businesses: Essential Tips is not a one-time project but a continuous journey of improvement and adaptation. As the digital world becomes more integrated, the risks will only continue to grow. However, by focusing on the fundamentals—employee education, multi-factor authentication, network security, and robust backup strategies—small businesses can build a formidable defense against the majority of cyber threats. Protecting your digital assets is synonymous with protecting your customers’ trust and your company’s future. Start by conducting a thorough risk assessment today, and remember that in the realm of cybersecurity, proactive prevention is always more cost-effective than reactive recovery. Stay vigilant, stay informed, and prioritize the security of your enterprise to ensure long-term success in an increasingly volatile digital age.